Google SSO Configuration
This guide walks you through configuring Google as an identity provider (IdP) for single sign-on (SSO) in Ask. This enables users to authenticate using their Google accounts.
Prerequisites
- Organization Admin access to Ask
- A Google Cloud Platform (GCP) account with project access
- Ability to create OAuth 2.0 credentials in Google Cloud Console
Step 1: Register a New OAuth Client in Google Cloud Platform
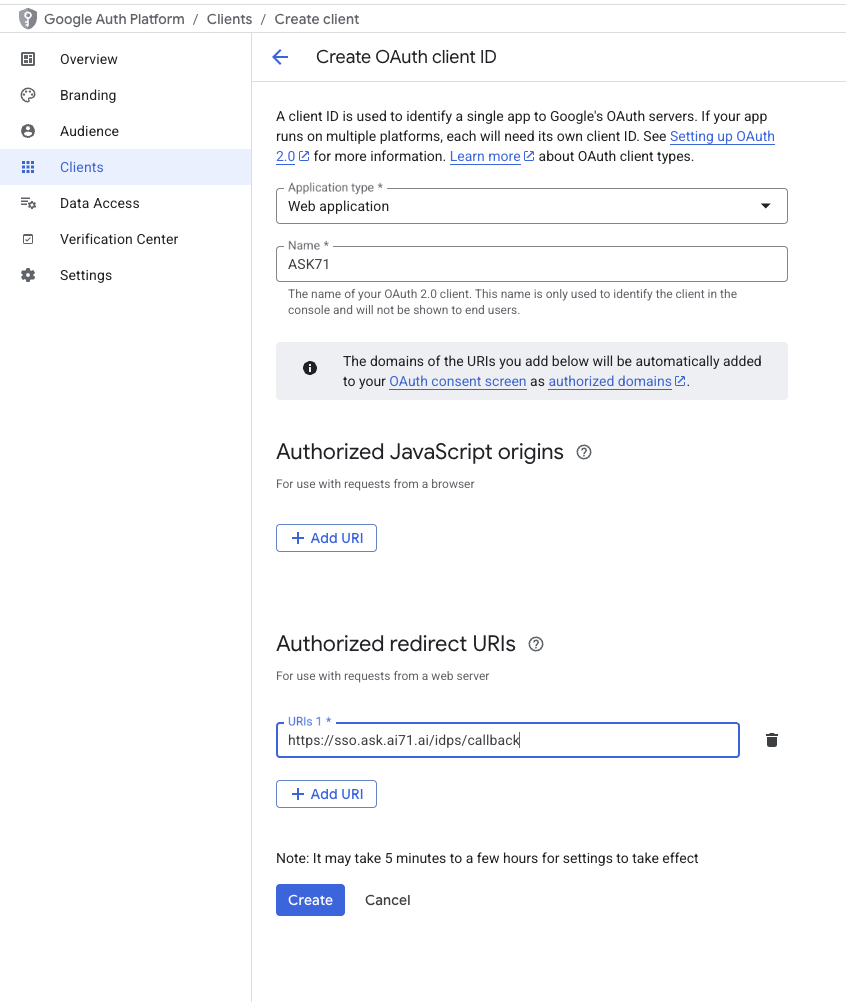
- Navigate to the Google Cloud Console Credentials page and select your project.
- Click "+ CREATE CREDENTIALS" and select "OAuth client ID".
- In the Application type dropdown, select "Web application".
- Enter a descriptive name for your OAuth client (e.g., "Ask SSO").
- In the Authorised redirect URIs section, add the Ask callback URL:
https://sso.ask.ai71.ai/idps/callback - Click "CREATE" to generate your OAuth client credentials.
Step 2: Retrieve Client Credentials
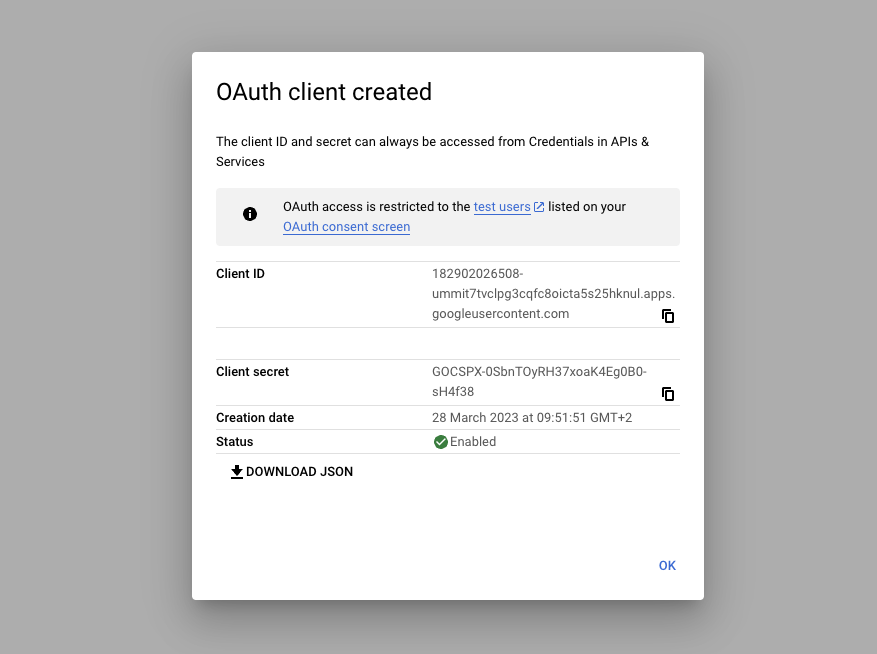
After creating the OAuth client, Google Cloud Console will display your Client ID and Client Secret. Save these credentials securely, as you'll need them in the next step.
Step 3: Configure Google SSO in Ask
3.1 Navigate to Security Settings
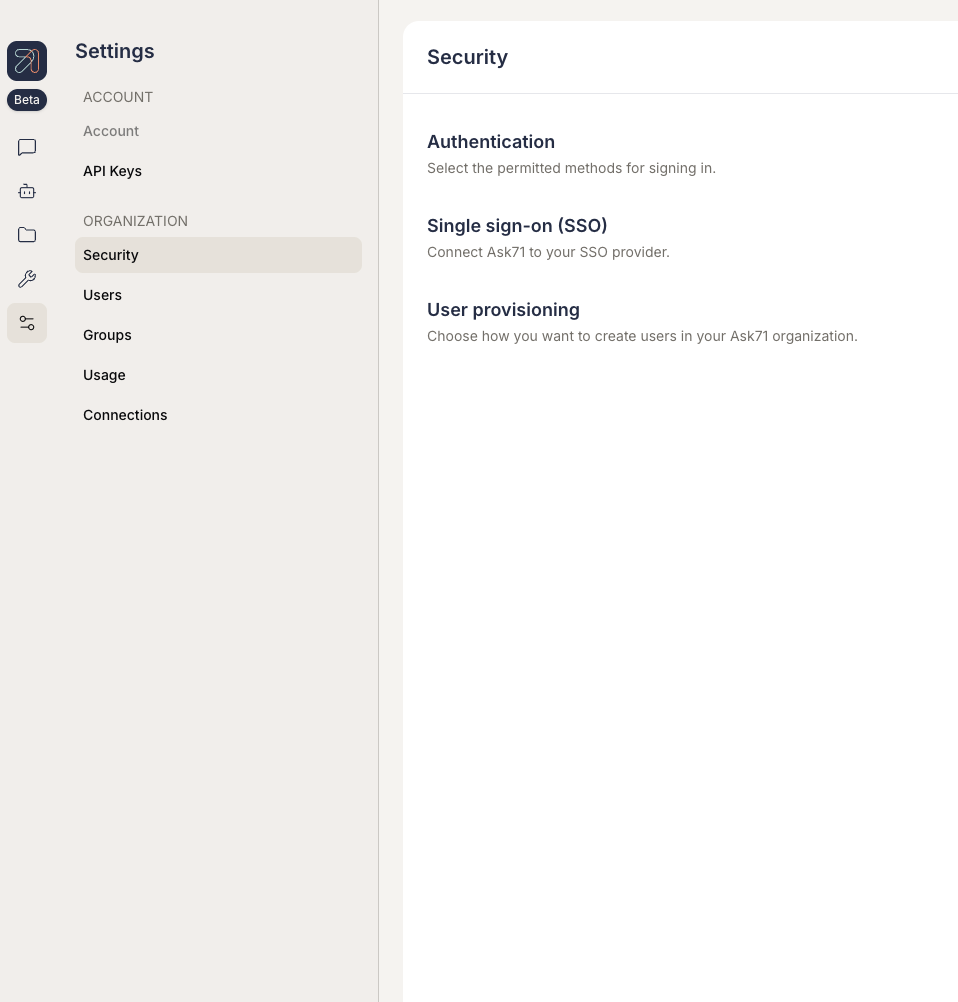
- Log in to Ask as an Organization Admin.
- Navigate to Security in the organization settings.
3.2 Select Google as Identity Provider
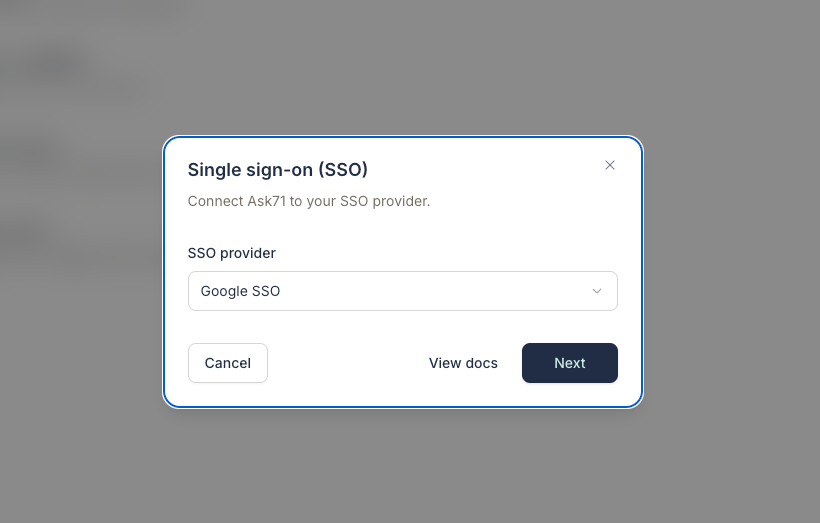
- In the Security settings, locate the Single sign-on section.
- Select Google from the available identity provider options.
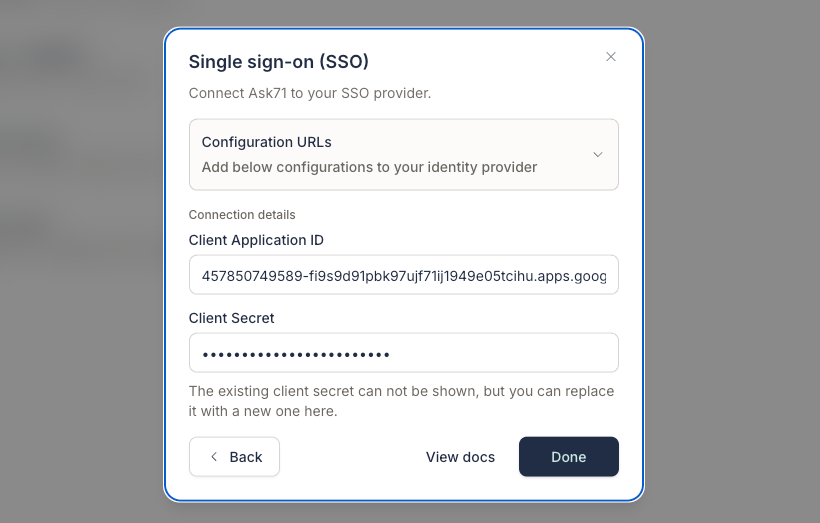
3.3 Enter OAuth Credentials
- Enter the Client ID from Step 2.
- Enter the Client Secret from Step 2.
- Click Done to save the configuration.
3.4 Fetch the Callback URL
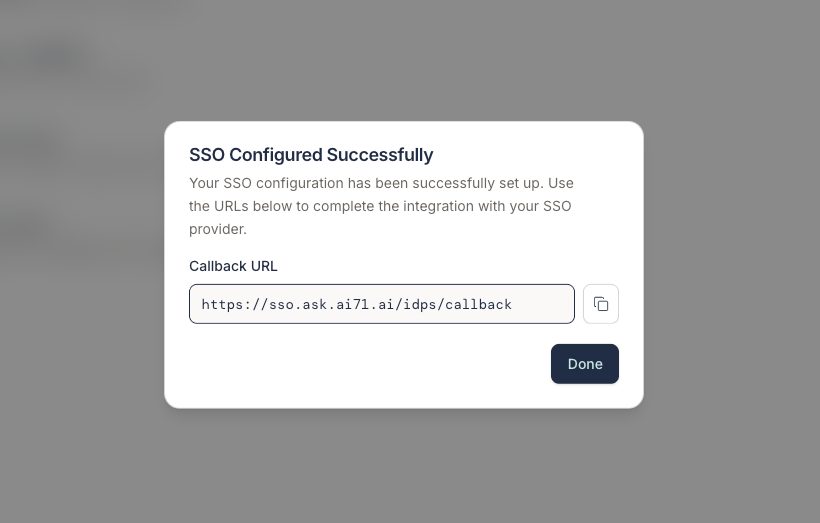
After saving the credentials, Ask will provide a callback URL that you need to use in your Google Cloud Console configuration. Ensure that this URL matches the one you entered during OAuth client registration.
3.5 Enable SSO Authentication
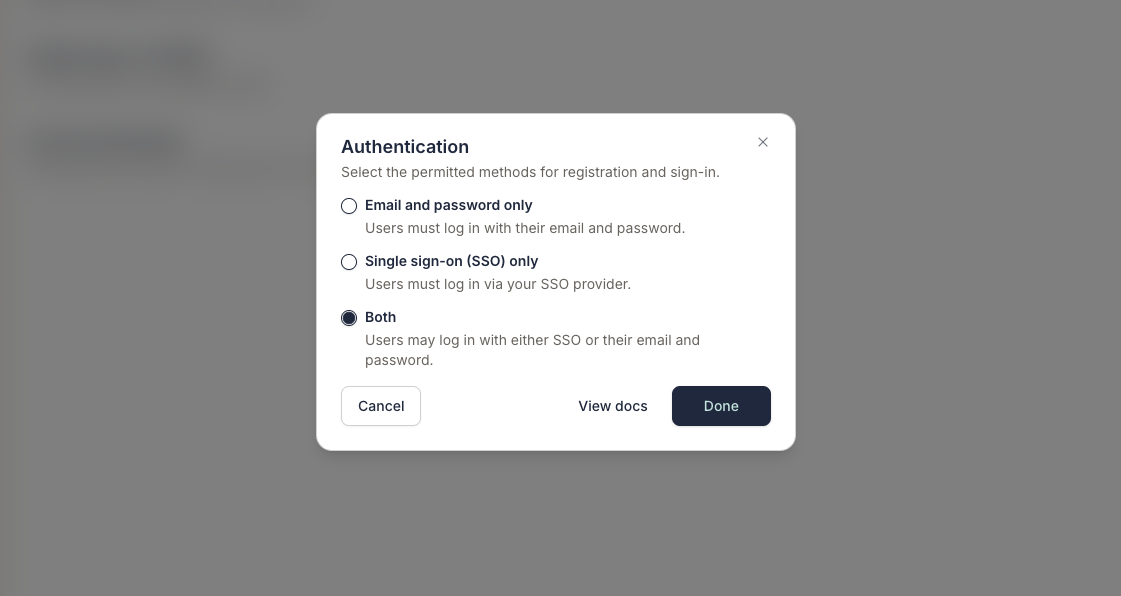
After configuring the Google identity provider, you must enable SSO for your organization:
- Navigate to Security > Authentication.
- Select the appropriate authentication option to enable Google SSO.
Step 4: Verify the Configuration
To verify that Google SSO is configured correctly:
- Open an incognito or private browsing window to avoid cached authentication.
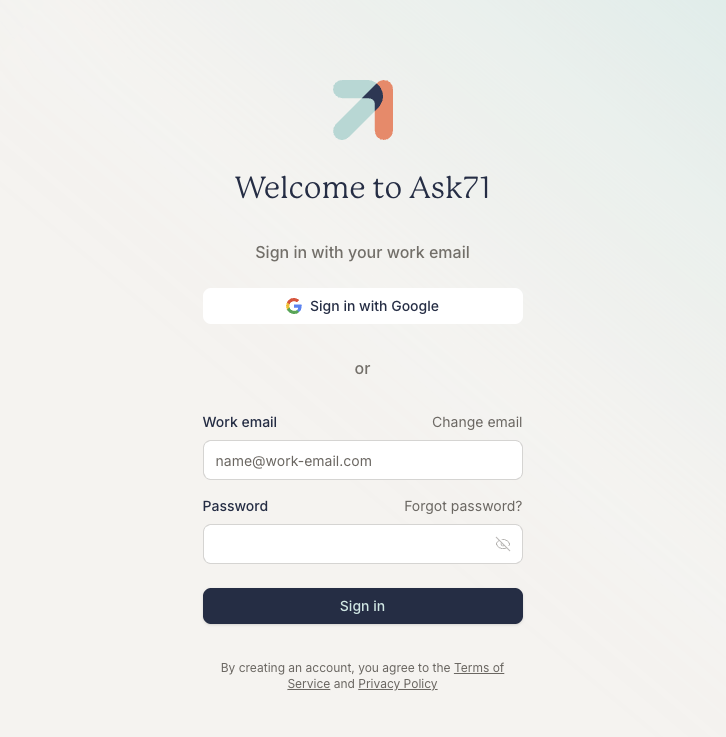
- Navigate to your Ask login page.
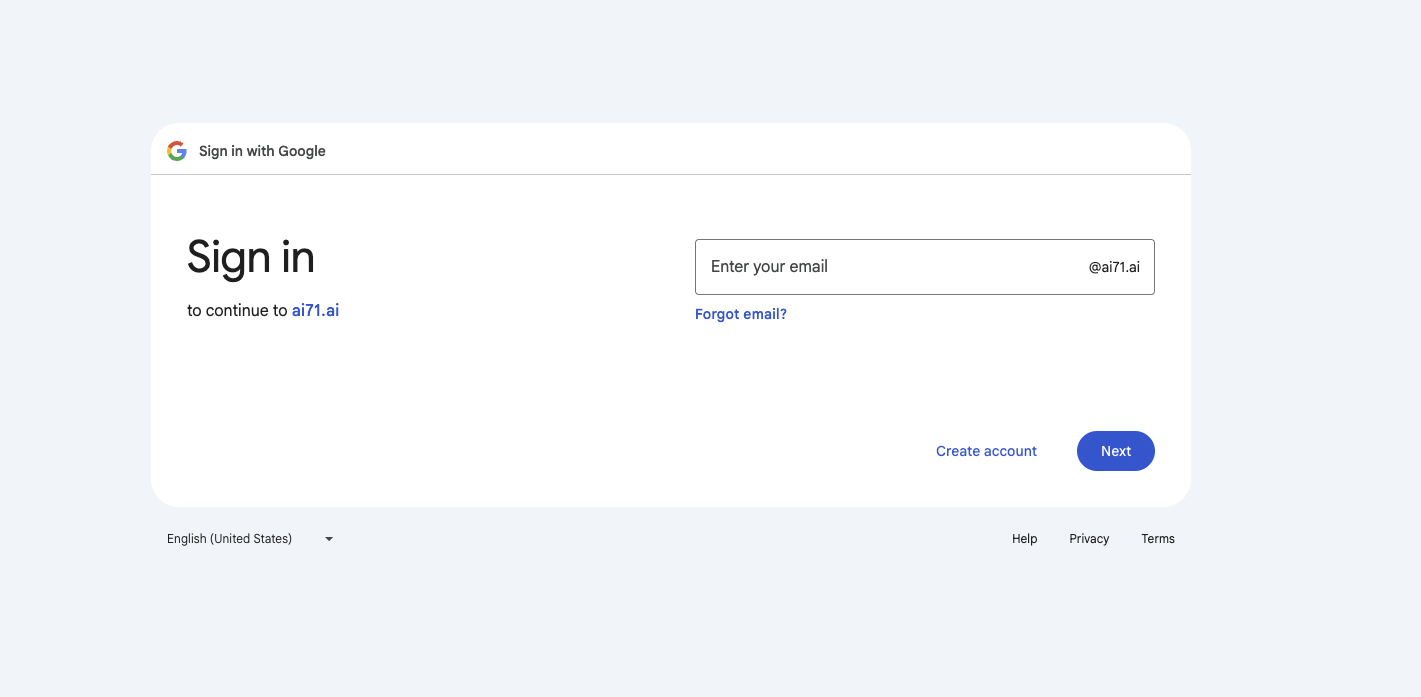
- You should see a "Sign in with Google" button or similar Google authentication option.
- Click the button to verify it redirects to Google's authentication screen.
- Complete the authentication flow using valid Google credentials.
Troubleshooting
If you encounter issues during setup:
- Verify callback URL: Ensure the callback URL in Google Cloud Console exactly matches
https://sso.ask.ai71.ai/idps/callback. - Check credentials: Verify that the Client ID and Client Secret are entered correctly without extra spaces or line breaks.
- Review OAuth consent screen: In Google Cloud Console, ensure your OAuth consent screen is properly configured for your application.
- Check API scopes: Ensure the required OAuth scopes (
email,profile,openid) are enabled for your application. - Test in incognito mode: Use an incognito window to avoid cached authentication interfering with your tests.
- Check expiry: Ensure the client secret hasn't expired and regenerate if necessary.